
Developers › A Journal from Behind the Trenches
Microsoft plays dirty against other browsers in Russia
Our Russian community manager Ilya noticed that members of our Russian forums made an interesting discovery on Microsoft's Russian site. If you open the page with a different browser than IE, you will get a popup ad for Internet Explorer. That's not necessarily wrong in itself, of course. The problem is that they are combining it with false claims about security.
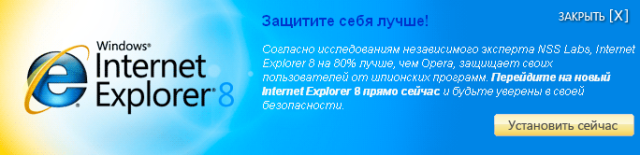
They seem to be saying that IE is 80% safer than Opera, or that it protects its users against spyware 80% better. This is based on an old and debunked report by NSS Labs.
If you visit the site with Chrome, the claim is perhaps even more exaggerated. It seems to claim that IE8 is better than any other browser at protecting its users from spyware and stolen passwords. Again they rely to NSS Labs and the debunked report they published.
The question is: Why is Microsoft publishing false claims from a report which is based on pseudoscience and manipulated statistics?
If you understand Russian, Ilya has more in Opera's Russian language blog.
Readers' comments 19
Left under the original article, as archived.
About this article
| Published in | A Journal from Behind the Trenches |
|---|---|
| Date | February 27, 2010 |
| Author | Haavard |
| Tags | opera, nss labs, russia, fud, misinformation, microsoft |
| Original | Internet Archive |
Kyle BakerSaturday, February 27, 2010 10:24:44 AM
FavSaturday, February 27, 2010 10:25:37 AM
metudeSaturday, February 27, 2010 11:43:09 AM
Maybe, ie 8 safer than opera 3.0
PurdiSaturday, February 27, 2010 12:02:39 PM
Originally posted by DjiXas:
It's called lying. Yes, Apple lies too. So that means it's OK for Microsoft to lie?
Did you even read the blog post? It refers to the dishonest hit piece by NSS Labs. There's even a link to the article that debunks it!
Why do you always attack Opera, DjiXas?
Kai OckendorfSaturday, February 27, 2010 1:48:08 PM
MarcoSaturday, February 27, 2010 2:19:33 PM
http://techie-buzz.com/softwares/recover-saved-passwords-in-opera.html
is there some place to report it?
Krio LythSaturday, February 27, 2010 2:21:55 PM
PurdiSaturday, February 27, 2010 3:03:01 PM
Originally posted by myeagle:
What on earth does this have to do with the blog post? It isn't even something that needs to be "reported".
FavSaturday, February 27, 2010 3:56:50 PM
Originally posted by Purdi:
No, not a fan of dirty tactics either. However, maybe then it's about time to take more serious action than just post on a blog?
"Misleading or False Advertising"
PurdiSaturday, February 27, 2010 5:13:17 PM
Originally posted by DjiXas:
Somehow I doubt that just any random Opera employee has the power to take any kind of action.
Also, a blog post is a good thing because it lets people know what's going on. That way Microsoft can't get away with it in silence.
Rafael LuikSaturday, February 27, 2010 5:20:54 PM
AsiresSaturday, February 27, 2010 6:26:48 PM
Cutting SpoonSaturday, February 27, 2010 8:39:35 PM
Besides, if all they are relying on is the rare voluntary trojan, that old report was moot. (since being infected merely by loading the page is the biggest failure of IE and 'Fox)
Charles SchlossSunday, February 28, 2010 6:54:08 AM
Microsoft needs to clean up their act and help the web forward and not push it back
João EirasMonday, March 1, 2010 1:36:13 PM
Originally posted by Marco:
What's the problem? That utility just uses the same algorithm that Opera uses to read the passwords' file. If you want real protection, you must define a master password.
MarcoMonday, March 1, 2010 2:14:20 PM
Techie Buzz Verdict
If an external software can crack the
algorithms of these browsers and fetch
the passwords, it would definitely be good if they can provide an option to set a master password and access the stored passwords, rather than having a algorithm which can be cracked easily.
That said, OperaPassView is a really
handy software to have, but again it
exposes the vulnerabilities of a
browser. What if your laptop is lost?
Anyone could use software like these
and get access to your passwords.
Are you listening Google Chrome and
Opera?
That's what I thought you advanced tech users see at first glance in the article, for I seen a similitude with MS advice , "don't use this browser cause there are better safe alternatives"
But I must be wrong, sorry to wasting your time,
@Purdi
When I said a place to report the article I mean if here in the Community exist a Forum or Blog to discuss what is reviewed in the web about Opera.
PurdiMonday, March 1, 2010 2:43:18 PM
Originally posted by myeagle:
Then that average user is wrong. Did you even read the comments?
Are you trolling?
If not, why are you repeating this drivel when you have already been informed that Opera already has a master password feature?
PatrickTuesday, March 2, 2010 8:23:26 AM
Originally posted by Purdi:
Exactly. Let's always make it clear that Lying and Marketing are two very different things even if completely unethical so called "Marketing Professionals" tend to get things confused way too often.
endless loveTuesday, March 2, 2010 2:31:54 PM